What Your Clients
Need Hardware Authentication For
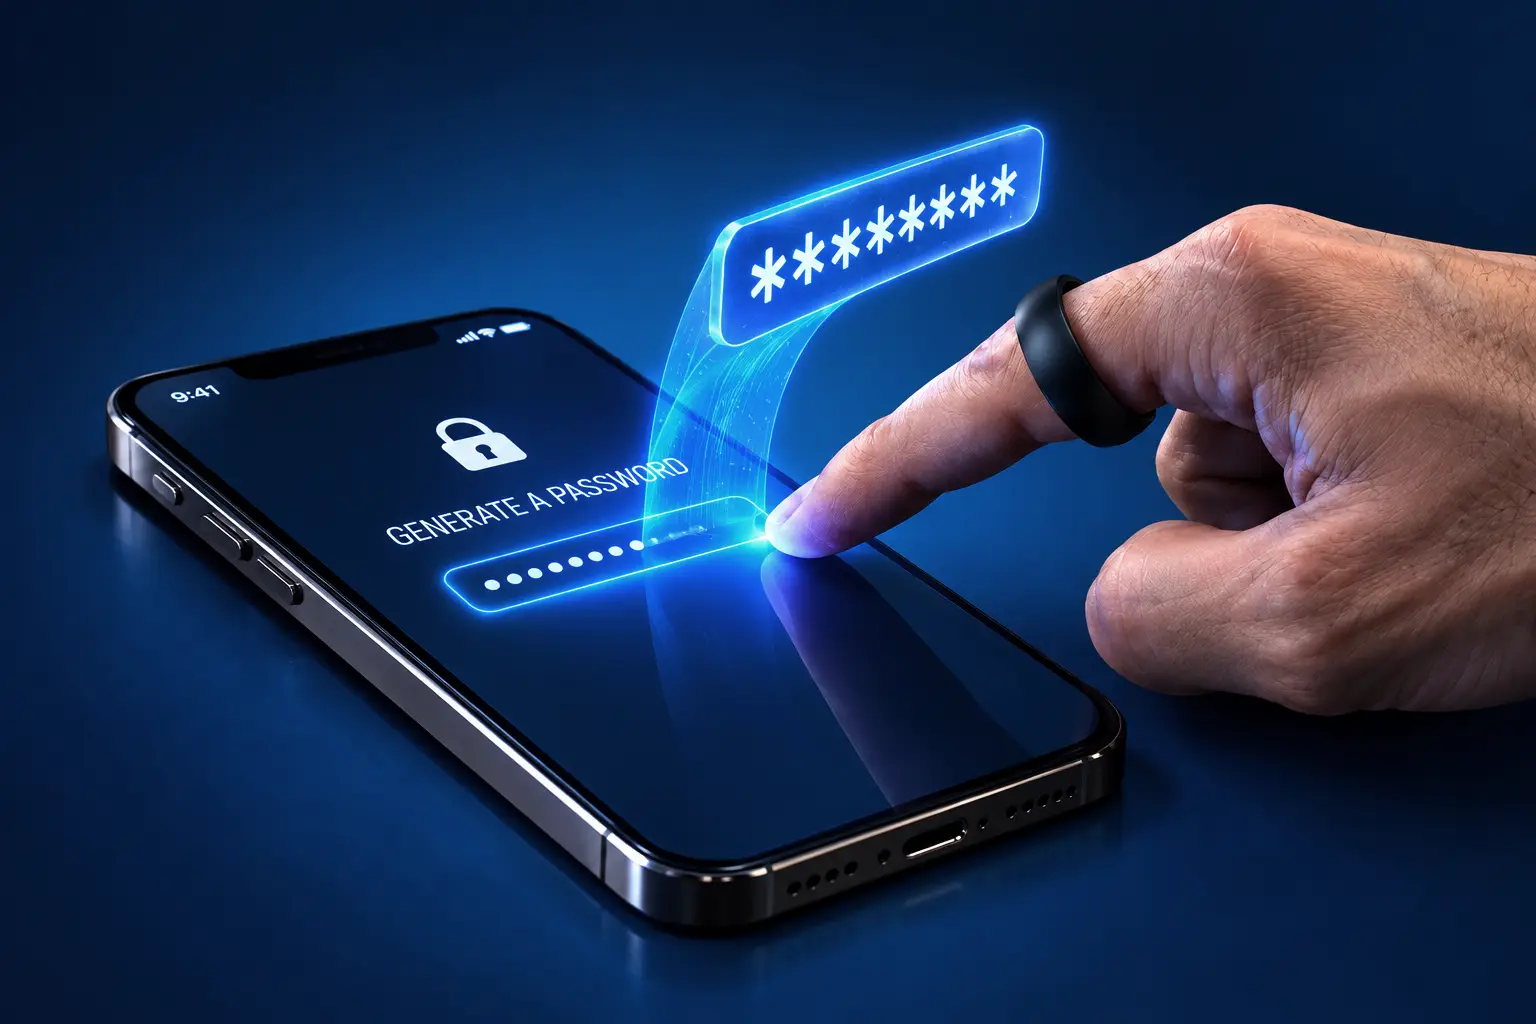
Eliminating password reuse across the organization
Most SME breaches still start with a reused or phished credential. Seedkeeper PRO generates and stores a unique strong password per account, offline, without a cloud vault that becomes its own attack surface.
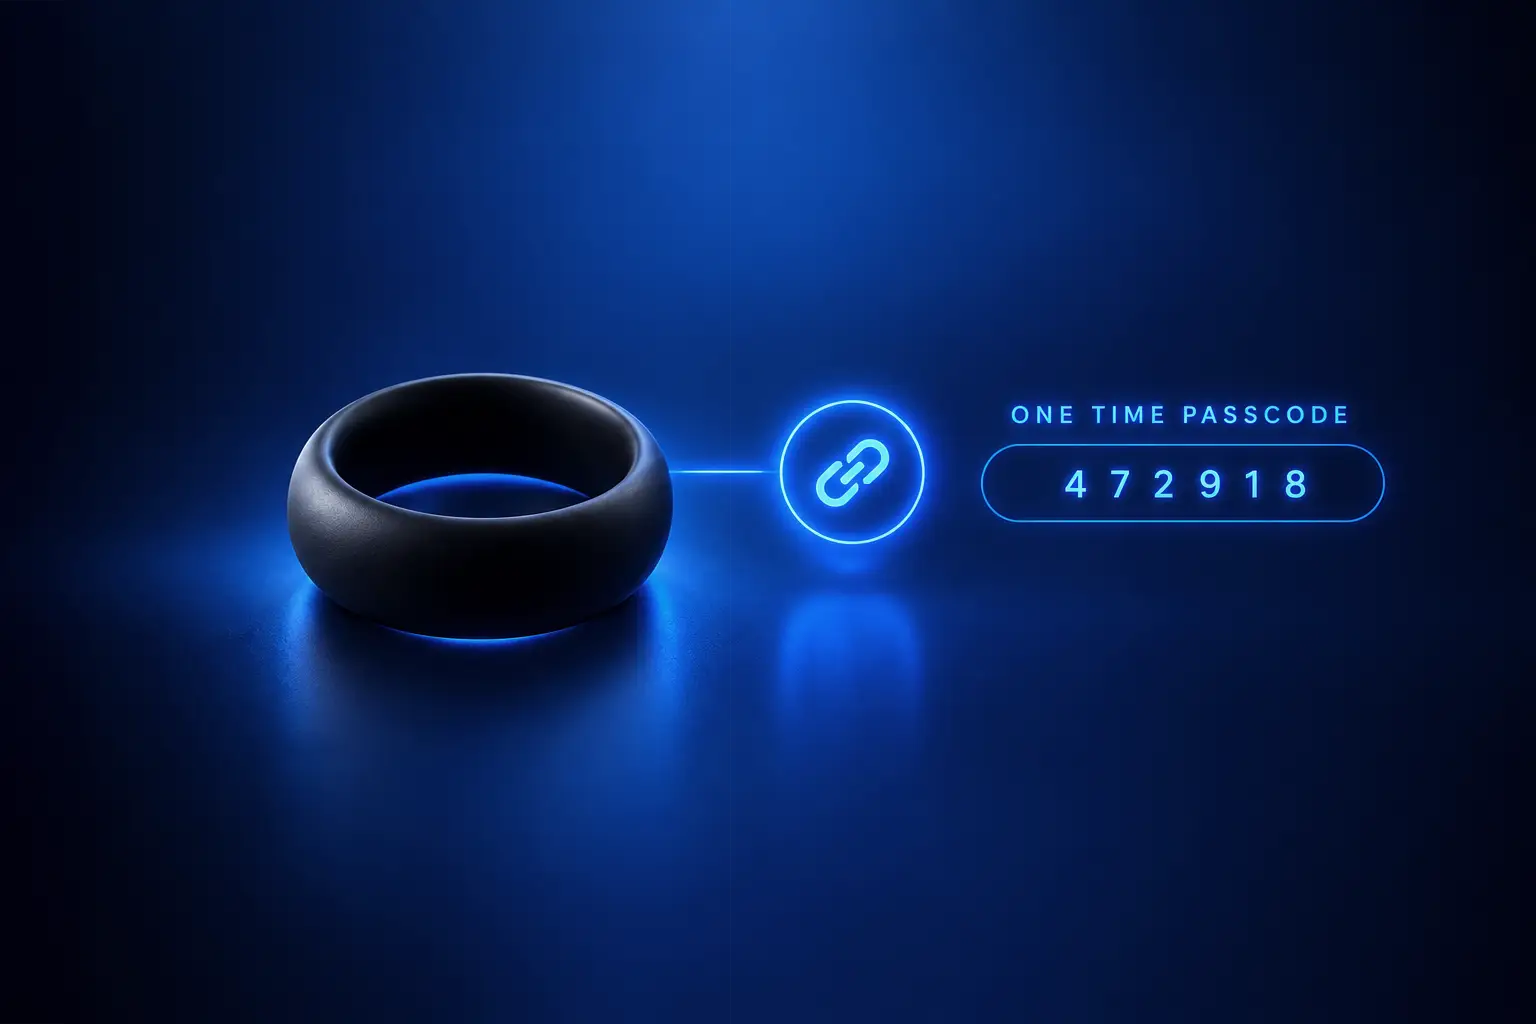
Replacing authenticator apps on personal phones
When 2FA lives on an employee’s personal device, the organization has no control over it – and loses access to it the moment that employee leaves or loses their phone. Hardware-based offline TOTP solves both problems in one device.
Passwordless login via passkeys for the whole team
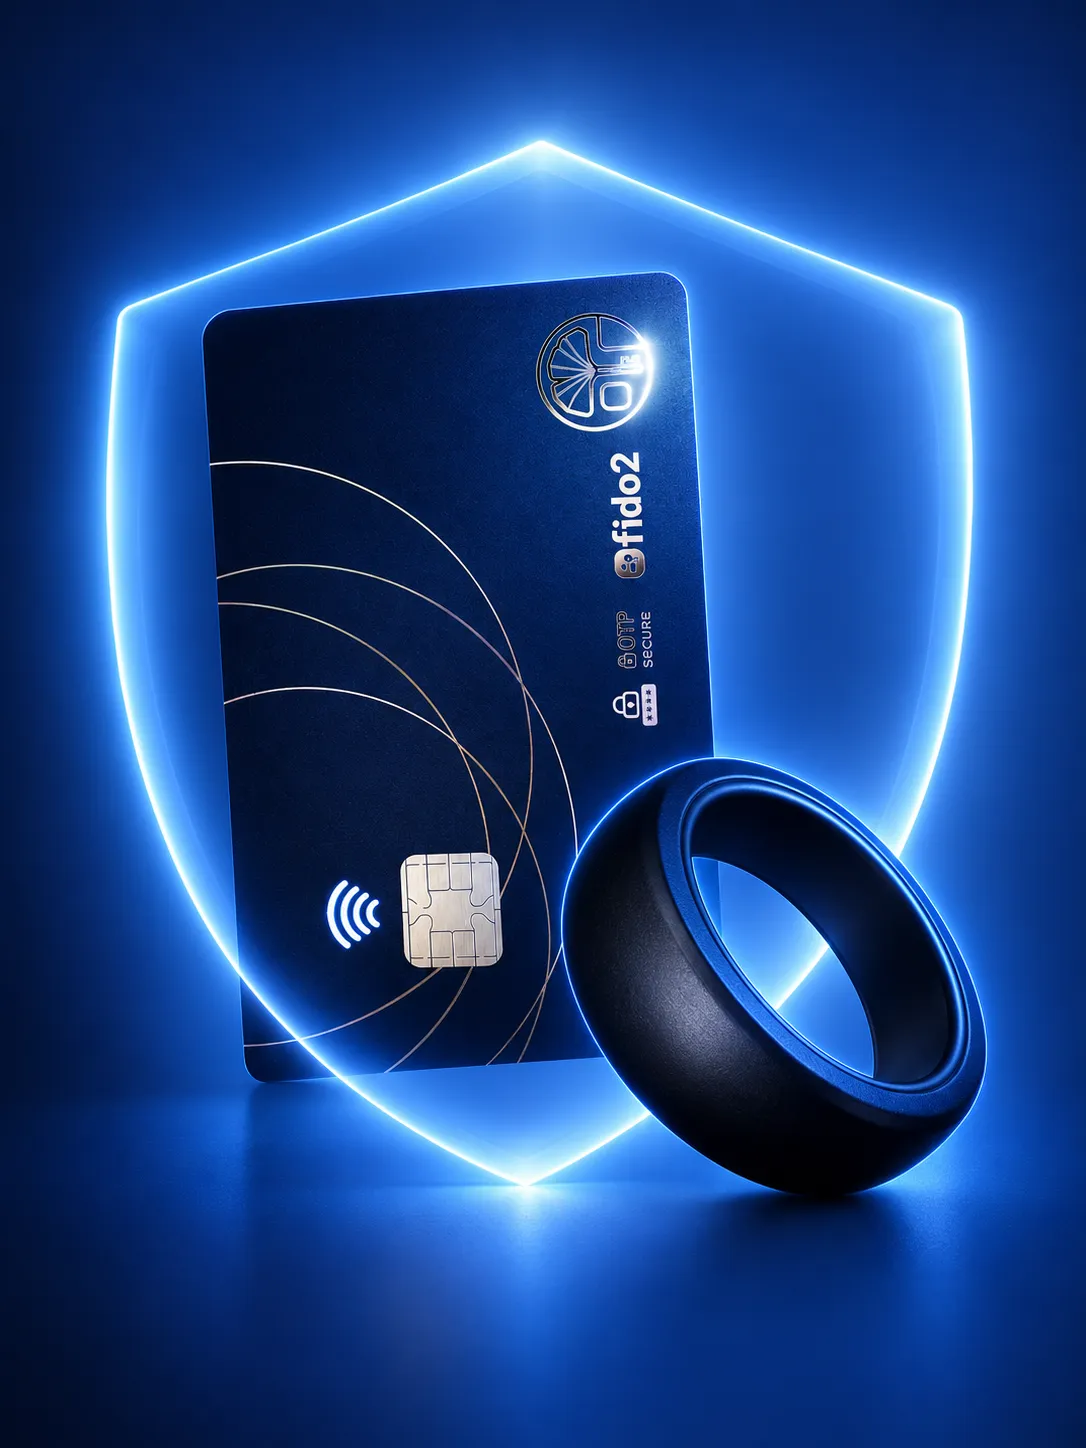
FIDO2 passkey authentication eliminates the phishable password entirely for supported platforms. For clients asking “how do we actually implement passwordless”, this is the hardware that makes it practical without depending on a vendor’s cloud sync.
Protecting critical admin and recovery credentials
Modern recovery phrases, SSH or PGP keys, API keys, emergency admin credentials… the secrets that, if lost or stolen, cause the most damage. Stored offline in a certified secure element, accessible only with PIN authentication. Backup is performed via encrypted device-to-device communication between two compatible devices.

Trusted by Security Providers Across Europe
Swiss crypto security specialist deploying Seedkeeper PRO for clients managing high-value digital asset credentials and recovery phrases.
Central European IT security integrator distributing Seedkeeper PRO as part of their hardware authentication offering to SME clients.
Piloted Seedkeeper PRO for employee authentication into internal and citizen-facing web applications, replacing password-based login with phishing-resistant FIDO2 authentication.
A growing network of Belgian cybersecurity consultancies deploying Seedkeeper PRO across SME client environments in Belgium and the Netherlands.